Posts

Building a threat model for a PaaS based Cloud service

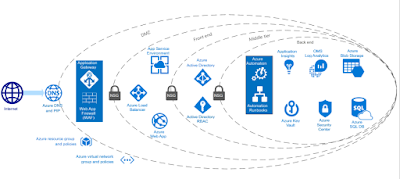
A while back I worked with a great Architect general guru of secure code. Adam Shostack who is a foremost expert when it comes to threat modeling . He does a great job in help educate us all in how you should plan a secure solution before you build it. A threat model should be seen as a key design element before code is started, similar to a floor plan in a house design. In this blog I wanted to illustrate the value and methods required to build a threat model, and tie it back to work I recently published, Payment Processing Blueprint for PCI DSS-compliant environments which included sample threat model for a cloud based PaaS solution. Wow, that’s great a free starter threat model to an architecture, what else can you ask for? What does it take to create your very own threat model? Think like an attacker, it’s important to see the problem from the attackers point of view when designing, or architecting a solution. For instance that includes thin...
PCI DSS workload in Azure, done in a snap.

Image
This past bit I've been working on a new set of solutions that expands on work I've done in the past helping people adopt Azure cloud securely. The process has involved an evolution that moved from guidance to automation. I've also written about shared responsibility and what it takes a provider like Microsoft to create a compliance program. But what does it take our customers to use our services and be compliant? The PCI Blueprint is the first of its kind solution, that makes it possible to quickly understand what it takes to build a compliant workload on Microsoft Azure without having to learn the ropes of PCI DSS compliance! I put together a short video that illustrates how easy it is to deploy the solution, and a PCI DSS workbook providing the mapping to controls for the solution (which you can download from the documentation site) What's also really cool is that the solution has a full fledged threat model diagram provided. If you've ever contemplat...

Azure Compliance papers - 8 month sprint to publish 8 papers

Image
It's been a while since I posted a blog. And to my readers I apologize. However in the past six months I've been madly working to publish 8 white papers on security and compliance for Microsoft Azure... It's a bit crazy to think anyone can get more than a paper published a month, especially when it requires as many reviewers as I've had to place my writing through. Normally, I place my ideas on the screen and bam... it's published!.. At my 'day' job it takes a bit more rigor to get a paper published. Including colleagues that are area experts providing feedback plus getting lawyers to validate that everything stated is in line with good corporate guidance. That normally means two months of reviews for everything I create. This is the first time I've tried to execute the writing, editing, reviewing and publication of 8 consecutive streams of content. It's true that the work is supper similar, and that's because it relates to compliance... And...

Enabling Azure security controls to help your ISO 27001 compliance effort

Implementing effective network security measure requires several monumental alignments. This includes things such as:  Budget - If security looks like an overhead to a company, it is. And with no budget security programs flounder… in fact I remember a time when security implementation was installing a 'firewall'. Management buy in and active participation- Security only works if participation is mandatory by all. Just because you have a corner office does not make you exempt from following the security rules. Turns out executives are usually the easiest target in an organization, because they don't see security measure apply to them, and they think they should have access to all corporate assets. Effective and easy to use security people, processes, and technical security controls. In other words if the security is difficult to implement, or use it will be avoided and bypassed. Compliance - The big C in secu...

Work on the CSA CCM 3.01 Azure entry

Hello everyone. Today my team released an update to the response Cloud Security Alliance's (CSA) Cloud Control Matrix (CCM) version 3.01 framework. It's quite phenomenal  level of work in getting such a massive document lifted revised, and posted.  Interested in the work, read the paper which is over 36 pages long and covers 130 controls. Here's what we announcement -  Microsoft Azure is proud to release our response to the Cloud Security Alliance's (CSA) Cloud Control Matrix (CCM) version 3.01 framework. The response document provides customers a straightforward process for evaluating Azure’s security, privacy and compliance capabilities and its commitments to trust and transparency using industry-accepted standards and practices. In addition, the CCM—and its entry into the CSA Security, Trust, and Assurance Registry (STAR)—provides a “one stop shop” offering a comprehensive guide addressing standard requests for information that cloud adopters need in orde...

A Practical Guide to Designing Secure Health Solutions Using Microsoft Azure

Today I have finished publishing my latest great work of security and compliance content. Check it out!. A Practical Guide to Designing Secure Health Solutions Using Microsoft Azure whitepaper providers readers considerations guidance for using cloud technology, includes risk management, shared responsibility considerations, establishing an information security management system, understanding industry and local regulations, and establishing standard operating procedures. It outlines, and provides recommendations to 13 security principles that are both aligned to a standard information security management standard, such as ISO 27001, and standard development processes, such as Microsoft’s Security Development Lifecycle (SDL). The paper also gives readers a direct view of the key principles by applying them to a ‘lift and shift’ health based case study. Whitepaper Table of Content Compliance and security methodology   Standard operating procedures Incorporat...

Team Ghost Shell returns

While doing a bit of reading recently I ran across this interesting story about Teamghostshell an active hacking group that has come back to life on June 29th after a couple of years of silence. The groups recent exploited an extensive list of sites, which they disclosed on pastbin .  If you read the hacker team's extensively long diatribe you will get an impression that their motives are pure and for the benefits of society, but like all disclosures the only people that suffer are the victims found in the data drop. You can also distill from the dialog that they probably used several COTS exploit kits, and it seems that these involved extensive use of cross site scripting attacks. What interested me in particular is that in 2012 when the team supposed 'peace treaty' and extensive hiatus they included a data dump of a host that they compromised.  The host information was listed as -    Server Type: Apache/2.2.3 (Red Hat) What is noteworthy to me is...